Resilience is not a product. It is a posture.

Varde Advisory provides independent cybersecurity and resilience leadership to boards and executive teams navigating regulatory complexity, operational risk, and uncertain conditions.

Latest signal 12 Oct 2026
operational

Attackers take over internet-exposed refrigeration controllers in about 700 French supermarkets

Watchtower Open →
Readiness over reaction• Independent by design• Built for uncertain conditions• Board-level accountability•

Independent by design.

We assess, plan, and prepare. Every engagement is grounded in regulatory reality and built for board-level accountability.

The firm is named after the Old Norse varðr, a stone cairn placed on high ground to mark safe passage and warn of danger. The operating logic is the same: clear signals, objective assessment, no vested interest in any vendor or platform.

We do not sell software. We do not chase trends. Independence is the structural precondition for honest assessment, not a tagline.

NIS2DORAISO 22301ISO 27001

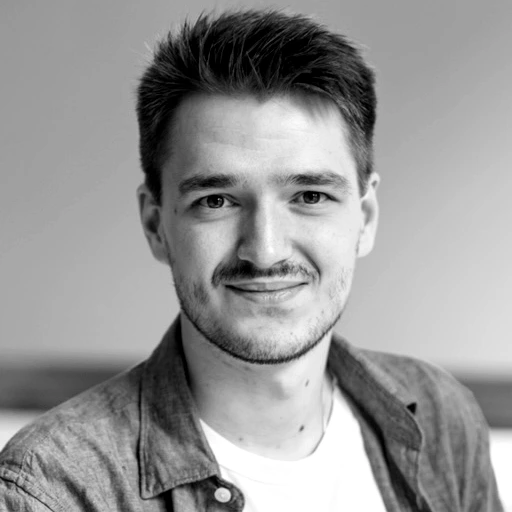
Philipp Classen

Principal Advisor, Varde Advisory

A career at the intersection of information security, operational resilience, and board-level accountability. Before founding Varde Advisory, Philipp led security and resilience programmes across logistics, energy, and automotive, reporting directly to group boards and navigating the regulatory frameworks that define European critical infrastructure.

Board-level cybersecurity advisory covering posture assessments, regulatory exposure analysis, and resilience strategy for NIS2- and DORA-bound enterprises

Programme governance including crisis decision-making frameworks, IT carve-out execution, and multi-year transformation oversight across multiple jurisdictions

Field-tested in crisis simulation, third-party risk, and critical infrastructure protection, validated through live exercises with executive leadership teams

CBCP · PMP

Utrecht, Netherlands · English & German

Founder portrait

Fractional CISO

Strategic security leadership at board level. We provide independent oversight, governance architecture, and stakeholder alignment. Grounded in the operational reality of running security programmes inside multinationals, not just writing about them from the outside.

View field report →
Minimum Viable Company Programme

Enterprise resilience under pressure. We define the critical functions your organisation must retain under severe conditions and test the assumptions your continuity plan relies on. Using dependency mapping and live scenario validation, not theoretical frameworks alone.

View field report →

Continuity & Recovery

Resilience architecture and operational readiness. Board-facing recovery strategy and pressure-testing of stated capabilities. Backed by tabletop exercises, runbook validation, and live crisis simulation for catastrophic scenarios.

View field report →

Strategic Project Management

Programme governance for critical transformations. We establish board-level oversight, clear decision rights, and accountability structures for security and resilience programmes. Disciplined execution that keeps initiatives on course without adding organisational drag.

View field report →

Output, not theatre.

Four engagements. Four outcomes. No projections, no marketing claims — only what was done, what was found, and what changed.

Read the field reports →
0months of policy & documentation backlog cleared
0sites brought under a Minimum Viable Company definition
0hrevenue-critical RTO, down from 72h

Make the hard call earlier.

The method in practice →
01

Discovery

An initial conversation to understand your situation, urgency, and stakeholders. No commitment, no proposal. Just clarity on whether we are the right fit.

Output: Go / No-go · 60 min · No commitment
02

Scoping

Defined boundaries: scope, deliverables, and cadence. A written proposal details fees, decision rights, reporting, and milestones. Engagement begins upon acceptance.

Output: Signed proposal · Fixed scope & fees
03

Engagement

Advisory engagement at executive level: board briefings, governance reviews, and operational programme oversight, with a structured cadence and direct access to the principal advisor.

Cadence: Board briefings · Direct principal access
04

Handoff

Knowledge transfer and capability handover. Where needed, we support the appointment of permanent leadership or transition to a lighter advisory retainer.

Output: Full handover · Retainer optional

Continuity & Recovery engagements run on OpenResilience, our in-house BCM platform.

What does NIS2 mean for my board?

NIS2 expands cybersecurity obligations to a broader set of sectors and introduces stricter management accountability. For boards, it means documented risk oversight, reporting timelines, and supply-chain due diligence. We translate the directive into a board-ready gap assessment and remediation roadmap.

Do you sell security products or software?

No. Varde Advisory is vendor-independent. We do not earn commissions from vendors or receive referral fees. Our recommendations are based solely on your risk profile, regulatory requirements, and operational constraints.

How quickly can advisory security leadership begin?

Most engagements begin within one to two weeks of a signed engagement letter. For urgent regulatory deadlines or incident response, we prioritise rapid mobilisation, sometimes within days, depending on current commitments.

What is a Minimum Viable Company Programme?

A board-level resilience exercise to determine which organisational functions must survive under severe disruption and whether the assumptions in your continuity plan hold under pressure. We validate through dependency analysis and live scenario testing, then align recovery priorities with financial and regulatory impact.

Is our data kept confidential?

Yes. We operate under strict confidentiality and non-disclosure agreements. Internal documents, assessment findings, and board materials are not shared with third parties unless explicitly authorised by you and required by law.

How do you differ from traditional security consultancies or the Big Four?

You work directly with the principal advisor, someone who has held operational security leadership roles inside multinationals, not only advised on them from the outside. Our output is a decision, not a deck. We do not deliver through large teams of junior analysts.

Initiate engagement.

LinkedIn
Varde Advisory